

Germany
7 regulators · 16 laws & regulations · 12 obligations · 36 enforcement actions · 1 upcoming deadline
Germany, which falls within the Western European region, is a major player in the global economy and has a very stable democratic system divided into 16 federal states that are sovereign.
Regulatory pulse · 90 days
Laws & Regulations Enforcement NewsOverview
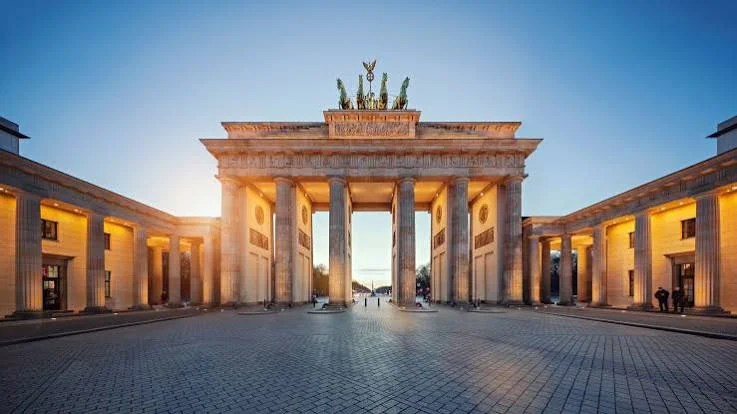
Germany, which falls within the Western European region, is a major player in the global economy and has a very stable democratic system divided into 16 federal states that are sovereign. The heart of German culture and history is the Brandenburg Gate, which is a masterpiece architecture and an important symbol of the unity and freedom of Germany in the world at large. In terms of regulations, Germany has a well-structured governing system that is well incorporated into the European Union’s standards. As far as RCGS is concerned, there is strict regulation in Germany, with BaFin being the main regulator.
The compliance environment is greatly dominated by Anti-Money Laundering and Countering the Financing of Terrorism (AML/CFT). Financial institutions that exist in this jurisdiction encounter a strong structural pressure to have a robust AML compliance program. This AML compliance program acts as a continuous obligation with real-time timing values for tracking of the customers and automated transaction monitoring. In accordance with the laws of Germany—which are quite similar to those of France in terms of their monetary and financial code—organizations must have stringent Customer Due Diligence (KYC/CDD) standards, which can be upgraded to Enhanced Due Diligence (EDD) with respect to the Politically Exposed Persons (PEPs) or corporate structures. Moreover, the reporting of the Suspicious Transactions is an absolute event-triggered obligation.
Concerning the protection of data and privacy, Germany ensures compliance in terms of the convergence of financial monitoring together with GDPR under the German Federal Data Protection Act (Bundesdatenschutzgesetz - BDSG). The duty to ensure a lawful basis and the provision of clear privacy notices is considered an operational necessity. Although there are some individual privacy rights, like the right to erasure, which override the GDPR as statutory exemptions, being subject to the mandatory requirement of 5 years' retention period for AML records, the data controller needs to be always ready to deal with data subject rights. The obligation of data breach notification is an important trigger framework, where companies are required to report to the competent supervisory body within 72 hours of breach discovery, and inform data subjects in cases of high-risk breaches.
| Law or regulation | Type | Year | Regulator | Source |
|---|---|---|---|---|
| Circular 09/2025 (VA) – Minimum requirements under supervisory law on the system of governance of insurance undertakings under Solvency II (MaGo für SII-VU) status not recorded | Circular | 2025 | BaFin | official |
| Kryptomärkteaufsichtsgesetz – KMAG (Crypto Markets Supervision Act) | Act | 2024 | BaFin | official |
| Regulation (EU) 2023/1113 on information accompanying transfers of funds and certain crypto-assets (recast) status not recorded | Regulation | 2023 | BaFin | official |
| DORA — Digital Operational Resilience Act (Regulation (EU) 2022/2554) | Regulation | 2022 | — | official |
| Law on Tracing Proceeds of Serious Crimes (Money Laundering Act - GwG) | Act | 2017 | FIU-DE | official |
| Supervisory Requirements for IT in Financial Institutions(BAIT) | Circular | 2017 | BaFin | official |
| GDPR (Regulation (EU) 2016/679) | Regulation | 2016 | BfDI | official |
| No instruments match these filters. | ||||
Recent enforcement
Open tracker →| Date | Entity | Regulator | Action | Source |
|---|---|---|---|---|
| Oct 2026 | Nomura Holdings Inc. | BaFin | Monetary Penalty | official |
| Oct 2026 | VW AG | BaFin | Monetary Penalty | official |
| Sep 2026 | Deutsche Bank AG | BaFin | Remedial Direction | official |
| Aug 2026 | pferdewetten.de AG | BaFin | Monetary Penalty | official |
| Aug 2026 | Two natural persons (not named) | BaFin | Monetary Penalty | official |
Industry compliance
Essential obligations
All obligations →| Obligation | Timing | Regulator | Source | Detail |
|---|---|---|---|---|
| Internal whistleblowing channel | Acknowledge within 7 days; feedback within 3 months | — | source | |
Section 12(1) HinSchG requires employers to ensure at least one internal reporting office, and section 12(2) applies this to employers normally employing at least 50 people (section 12(3) lists entities that must do so regardless of size). Under section 17, the reporting person gets an acknowledgement within seven days and feedback within three months of acknowledging receipt. Section 40(6) sets a fine of up to EUR 20,000 for not establishing an internal reporting office. |
||||
| NIS-2 cybersecurity risk-management measures | Continuous | BSI | official | |
Section 30 BSIG requires suitable, proportionate and effective technical and organisational measures, documented, and section 30(2) lists at least ten, including risk analysis, incident handling, business continuity, supply chain security, cryptography and multi-factor authentication. The BSI says responsibility for implementation and oversight lies with the management. |
||||
| AML compliance programme and officer | Ongoing | FIU-DE | source | |
In Germany, the AML compliance program and officer obligations under the German Money Laundering Act (GwG) and the Banking Act (KWG) entail an obligation that is continuous in nature and is distinguished by a continuous (real-time / daily) time value. The above obligations are mandated in Section 6 and Section 7 of the GwG, as well as the MaRisk circular issued by BaFin, in which all financial and non-financial obliged entities are obligated to create a continuous risk management system. This involves having a continuous risk management system, which entails the appointment of a Money Laundering Reporting Officer (MLRO / Geldwäschebeauftragter) with absolute executive authority to conduct continuous corporate surveillance. In terms of its operation, the continuous tracking is continuous within the organization's environment and consists of performing continuous automated screening of the global asset freezing database, continuous real-time transaction monitoring, and continuous analysis of risks within the organization (Risikoanalyse) to prevent the financial exploitation of the market. The above structural demands are overseen within a two-tiered arrangement by BaFin and Deutsche Bundesbank, where not observing these active daily controls attracts serious administrative penalties. |
||||
| AML record retention | 5 years | FIU-DE | source | |
According to the German Money Laundering Act (GwG), the Anti-Money Laundering Record Retention requirement is defined strictly as a retention requirement and is regulated by a fixed time period, namely 5 years. This statutory obligation, which has been established according to Section 8 of the GwG and clarified by BaFin, implies that obliged financial and non-financial institutions shall store customer due diligence (KYC), risk assessment, and transaction history in a reliable, unalterable form. In contrast to a general calendar plan, the five-year period will commence at the moment of closing of an account in the case of customer identification records and at the end of the execution year in the case of individual transaction records. The requirement guarantees that a full financial audit trail is entirely organized and available immediately for the BaFin, the Deutsche Bundesbank, the FIU, and the judiciary in the process of a money laundering investigation, irrespective of any GDPR requests for erasing data. |
||||
| Customer due diligence (KYC/CDD) | At onboarding + ongoing | FIU-DE | source | |
As per the German Money Laundering Act (GwG), the concept of Customer Due Diligence (KYC/CDD) is understood to be an obligation in real-time/daily terms [GwG, MaRisk]. This main compliance requirement, which has been developed pursuant to sections 10 to 15 of the GwG and interpretative guidelines by BaFin, requires that obliged financial and non-financial institutions continuously monitor their customer base rather than performing static identity verification [GwG]. The system functions in real time and ensures that all customer information, transaction patterns, and socio-economic information undergo dynamic monitoring, where automated checks are performed daily against the worldwide sanctions list and PEP database [GwG, MaRisk]. It is also characterized by various risk-based tempos of operation which range from triggering immediate update of data in case of suspicious transactions to conducting periodic reviews in accordance with the risk levels of clients [GwG, MaRisk]. All information must also remain fully auditable by BaFin and the Deutsche Bundesbank. |
||||
| Suspicious transaction reporting | Immediate | FIU-DE | source | |
In accordance with the German Money Laundering Act (GwG), the Suspicious Transaction Reporting regime refers to an event-based requirement driven by the strict time value of immediate / without delay. The legal requirement, which has been stipulated by Section 43 of the GwG and put in place through the German Financial Intelligence Unit (FIU), requires that as soon as a compliance officer or a Money Laundering Reporting Officer (MLRO) determines the existence of a suspicion that funds or a transaction is associated with money laundering, tax evasion, or terrorist financing, a formal electronic report shall be made immediately through the goAML portal. Contrary to the calendar-based procedure, this requirement shall arise only in response to the occurrence of an irresolvable transaction warning or risky conduct on the part of the client. Practically, the report shall be made before undertaking the transaction to afford the FIU or prosecutors regulatory powers to block or immediately after the execution of the transaction in case there is no absolute block. |
||||
| No obligations match these filters. | ||||
Quick links — official sites
- BBk — Deutsche Bundesbank
- BfDI — Federal Commissioner for Data Protection and Freedom of Information
- BaFin — Federal Financial Supervisory Authority
- FIU-DE — Financial Intelligence Unit (Germany)
- BT — German Bundestag
- BAFA — Federal Office for Economic Affairs and Export Control (Bundesamt für Wirtschaft und Ausfuhrkontrolle)
- BSI — Federal Office for Information Security (Bundesamt für Sicherheit in der Informationstechnik)
Newsletter
Get CRCGS Weekly
A free weekly email from the Centre for Risk, Compliance & Governance Studies: the week's regulatory news, new regulations, updated country profiles, and the Knowledge Hub's latest reading and events.