
Mauritius
4 regulators · 4 instruments · 6 obligations · 1 upcoming deadline
Mauritius emerges as one of the shining stars of Africa’s economic success stories, swiftly emerging as a country that has moved on from being a volatile and mono-crop economy at the time of independ…
Regulatory pulse · 90 days
Laws & circulars Enforcement NewsOverview
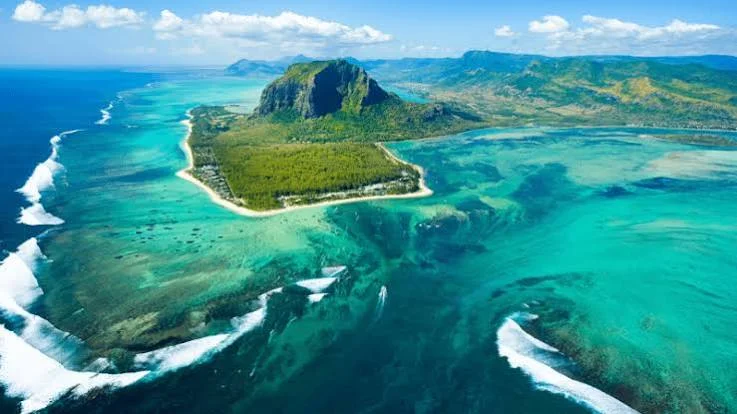
VERIFIED 29 SEP 2026Mauritius emerges as one of the shining stars of Africa’s economic success stories, swiftly emerging as a country that has moved on from being a volatile and mono-crop economy at the time of independence to becoming one of the most diversified and upper-middle-income economies in the region. Strategically positioned within the southwest part of the Indian Ocean, the nation-state has managed to position itself as a reliable financial link between the investments of Asia, Europe and the African continent. Its economy thrives on strong foundations that include financial services, tourism, information technology and manufacturing.
As far as risk is concerned, Mauritius is quite resilient on the macro level, although still vulnerable to a number of externalities. As it is a SIDS, the primary risk associated with Mauritius is environmental/climatic risk. It is highly vulnerable to sea-level rise, unfavorable weather, and tropical storms. As such, the coastlines of the country, which form the major source of income for the country (that is, tourism), are quite vulnerable. In addition, because it is an open and export-oriented economy, the country is also vulnerable to market risks.
The governance structure in Mauritius is remarkably stable and features a strong multi-party parliamentary democracy as well as an unwavering dedication to the principle of the rule of law. The presence of free and fair elections facilitates the sustenance of the democracy and smooth transfer of power. The nation follows an extremely robust hybrid legal system which combines English common law and the French civil code, offering a clean environment for the settlement of commercial disputes. This makes the nation a leader within Sub-Saharan Africa in terms of governance based on international benchmarks such as the Ibrahim Index of African Governance.
The country is renowned as a leading, clean international financial center in the sphere of compliance. After successful delisting from the FATF grey list, Mauritius has rapidly reformed the existing regulatory oversight. Both the Bank of Mauritius and the Financial Services Commission are very strict in enforcing the AML/CFT regimes. It is completely compliant with the international standards of OECD Base Erosion and Profit Shifting and keeps beneficial ownership registers. Through a focus on automated reporting, tax transparency, and cross-border regulatory compliance, the financial system of Mauritius is protected from illegal flows, and the country remains a safe and extremely competitive jurisdiction for foreign investment.
Who regulates what
View all →
Key laws & regulations
All Laws & Regulations →| Instrument | Type | Year | Regulator | Source |
|---|---|---|---|---|
| Data Protection Act 2017 | Act | 2017 | DPO | official |
| Financial Services Act 2007 | Act | 2007 | FSC | official |
| Banking Act 2004 | Act | 2004 | BOM | official |
| Financial Intelligence and Anti-Money Laundering Act (FIAMLA) | Act | 2002 | FIU-MU | official |
| No instruments match these filters. | ||||
Industry compliance
Essential obligations
All obligations →| Obligation | Timing | Regulator | Source | Detail |
|---|---|---|---|---|
| AML compliance programme and officer | Ongoing | FIU-MU | official | |
The laws in Mauritius are largely based on the Financial Intelligence and Anti-Money Laundering Act (FIAMLA), which requires obliged institutions to adopt a stringent and risk-based approach in detecting and preventing any form of financial crime, money laundering, terrorism financing, and proliferation financing. The obliged organizations are required to put in place internal controls; conduct obligatory customer due diligence and confirm the ultimate beneficial owner (UBO) at 25%; undertake continuous transaction monitoring, and keep compliance records for a minimum period of 7 years. There is a need to have a structure where institutions appoint an officer to act as the Compliance Officer (CO) to handle the daily compliance process, conduct business risk assessments, and arrange independent audits. On the other hand, there is a need for organizations to appoint an MLRO, who acts independently to evaluate the red flags and file suspicious transaction reports (STRs) to the FIU through the goAML system within 5 working days after detection of the anomaly. Failure to adhere to the requirements makes them susceptible to sanctions, which may include administrative sanctions of Rs 250,000 for structure violations, or criminal prosecution with penalties of Rs 10 million. |
||||
| AML record retention | 7 years | FIU-MU | official | |
As per Section 17F of the Financial Intelligence and Anti-Money Laundering Act (FIAMLA) of Mauritius, it is mandatory for the reporting institutions to maintain all compliance documents for a minimum duration of 7 years. The maintenance of these documents within the defined time frame makes it necessary that CDD documentation, identification document records, and account records are retained for a minimum of 7 years from the end of the business relationship. Likewise, individual transaction records, account books, and STRs whether internal or external have to be maintained for a minimum of 7 years since the completion of the transactions or reporting of the transactions. The records must be retained in such a manner that transactions can be reconstructed instantly and FIU and supervisory authorities can easily retrieve the historical asset trails. |
||||
| Customer due diligence (KYC/CDD) | At onboarding + ongoing | FIU-MU | official | |
The requirements on Customer Due Diligence (CDD) and Know Your Customer (KYC) are part of regulatory framework in Mauritius as per Financial Intelligence and Anti-Money Laundering Act (FIAMLA), regulated by Bank of Mauritius (BoM) and Financial Services Commission (FSC). All clients must be identified and verified using the strict threshold of 20% in order to identify the Ultimate Beneficial Owner (UBO) in the corporate structure. The process involves the application of the risk-based approach where Simplified Due Diligence (SDD) is applied to low-risk clients, whereas Enhanced Due Diligence (EDD) is used to high-risk clients or Politically Exposed Person (PEP), including verification of his Source of Wealth and Funds. Moreover, ongoing monitoring and periodic reviews should take place, depending on the risk level, ranging from annually for high-risk clients up to every four years for low-risk clients, and keeping transactions and identification data for 5-7 years. |
||||
| Suspicious transaction reporting | Event-based | FIU-MU | official | |
Suspicious Transaction Report (STR) under Mauritian law requires any suspicious activity that may be involved in money laundering, terrorist financing, and proliferation financing to be reported to the FIU using the electronic goAML system. STR is governed by the Financial Intelligence and Anti-Money Laundering Act (FIAMLA), which states that reporting entities should file an STR within a maximum period of 5 working days after determining reasonable grounds for suspicion by the Money Laundering Reporting Officer (MLRO); however, reporting within the day is highly recommended. STR is a very strict process that does not allow “tipping off” or informing the customer about reporting. The FIU can freeze funds for a maximum of 72 hours while doing analysis on transactions. Penalties for failure to report a suspicious transaction include a fine of MUR 1,000,000 and imprisonment for a term of 5 years, and in case of illegal disclosure, a fine of up to MUR 5,000,000 and a term of 10 years' imprisonment. |
||||
| Lawful basis, notice and data subject rights | Ongoing | DPO | official | |
Personal data protection in Mauritius is guided by the provisions of the Data Protection Act 2017 (DPA 2017) and regulated by the Data Protection Office, and the law is consistent with international practices [fscmauritius.org]. Under this legislation, the data controller has an obligation to ensure that there is a sound legal basis for processing the personal data, which can be consent, necessity for performing the contract or legal obligation. There is an obligation to present individuals with a clear Privacy Notice containing details of the reasons for the processing, the period of time for which the data will be retained, and the transfer of the information to other parties. The rights of the individual under DPA 2017 include the right of access, rectification, erasure, objection, and restriction of automated decision making. Failure to comply with these obligations results in criminal penalties of imprisonment and fines. |
||||
| Personal data breach notification | Event-based | DPO | official | |
The requirement for breach notification of personal data in Mauritius requires that the data controller notify the DPO of the breach without delay and, if possible, not later than 72 hours from discovering the breach. Under Section 37 of the Data Protection Act 2017, data processors shall notify the breach to their respective controllers immediately, and the controllers should notify the affected person directly if the breach involves a high risk to the rights and freedoms of the individual. The notification of the breach should detail the kind of breach, type of personal data involved, likely consequences, and measures taken to mitigate the breach. Failure to comply with breach notification requirements is considered a criminal offense and punishable by a MUR 200,000 fine and 5 years of imprisonment. |
||||
| No obligations match these filters. | ||||